
Cybersecurity · delivered by Nyoxa
Find the weaknesses before attackers do.
Authorized, methodical penetration testing of your real-world risk: web applications, APIs, cloud and everything of yours that faces the internet. No fear-selling, no jargon walls.
What we test
Six assessment services, one methodology.
-
 / 01
Web Application Pentesting
Manual, authorized testing of your web apps against real attacker techniques, not just scanner output.
-
 / 02
API Security Testing
Authentication, authorization, injection and logic flaws across REST and GraphQL APIs.
-
 / 03
Cloud & SaaS Review
Configuration and identity review of your cloud accounts and the SaaS tools your business runs on.
-
 / 04
Attack Surface Assessment
Everything of yours an attacker can reach from the internet, mapped, tested and prioritised.
-
 / 05
WordPress Security Audit
Hardening, plugin risk and configuration review for the platform most small businesses actually run.
-
 / 06
Email & Domain Security
SPF, DKIM, DMARC and domain posture, so your name is harder to spoof and your mail lands.

How a test runs
Authorized. Methodical. Retested.
Every engagement starts with written authorization and clear rules: what is in scope, what is off limits, and when testing happens. Then we work the target the way a real attacker would, manually, with tooling where it helps.
- Written scope and authorization before any testing
- Findings ranked by real business impact
- Fix-ready guidance your developers can act on
- Free retest of fixed findings
What you receive
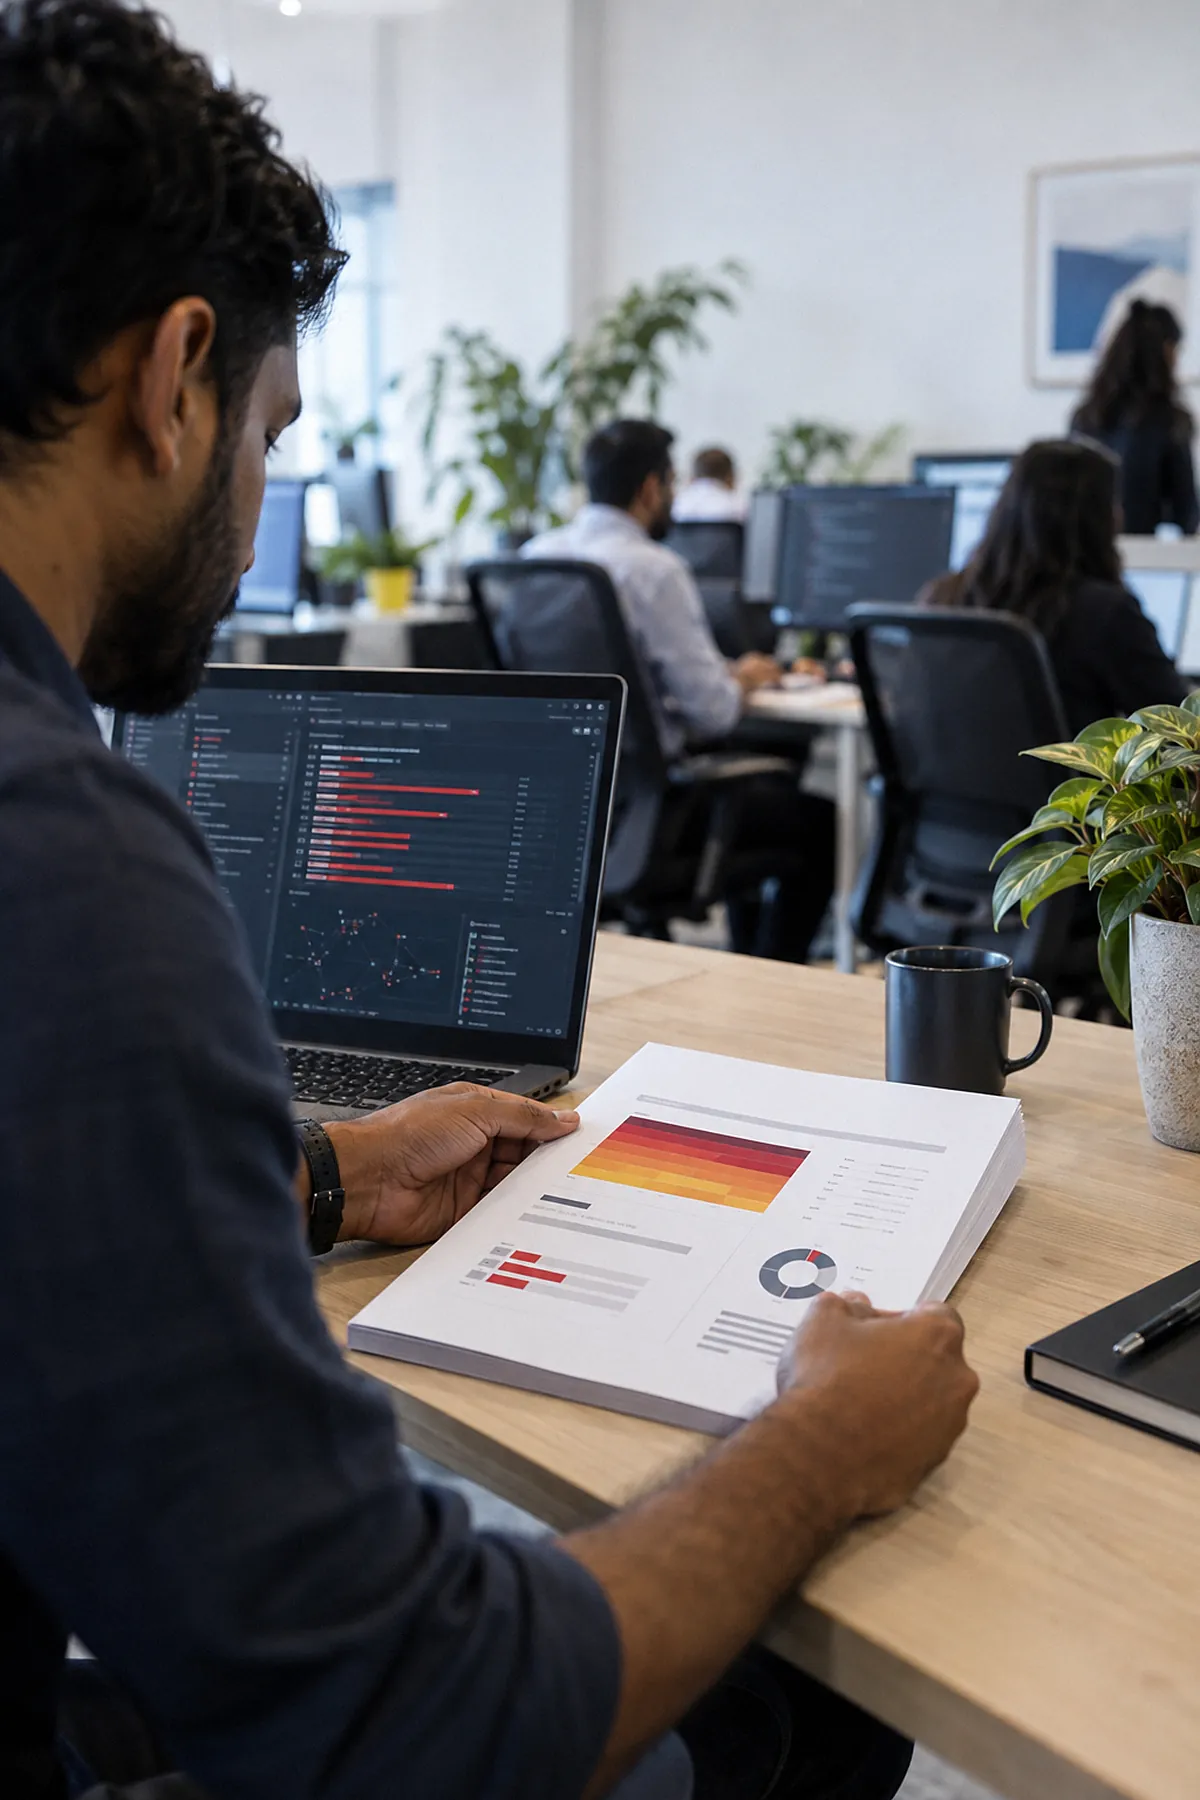
Deliverables built for decisions.
Contents
- 1Executive summary in plain language: what is broken and what it means for the business
- 2Technical findings with reproduction steps and evidence
- 3Prioritised remediation plan, ordered by risk, not by tool output
- 4Retest report confirming what was fixed
Fair questions
- Is this legal and safe for production?
- Yes. Nothing is tested without your written authorization and an agreed scope. Testing windows, excluded systems and emergency contacts are set before we start, and destructive techniques are never used against production.
- Will it disrupt our business?
- Assessments are planned around your hours and rate-limited to avoid load. Most clients notice nothing until the report arrives.
- We already run a vulnerability scanner. Why this?
- Scanners find known patterns. Attackers chain logic flaws, misconfigurations and weak assumptions that scanners cannot see. Manual testing finds the paths a scanner never will, and tells you which ones actually matter.

Start here
Know where you stand.
Tell us what you run and what worries you. We reply with an honest scope and a fixed price within one working day.
Scope an assessment